Backups Are Not Enough: How to Verify Disaster Recovery
A successful backup does not prove recoverability; test restores and validate RPO/RTO.
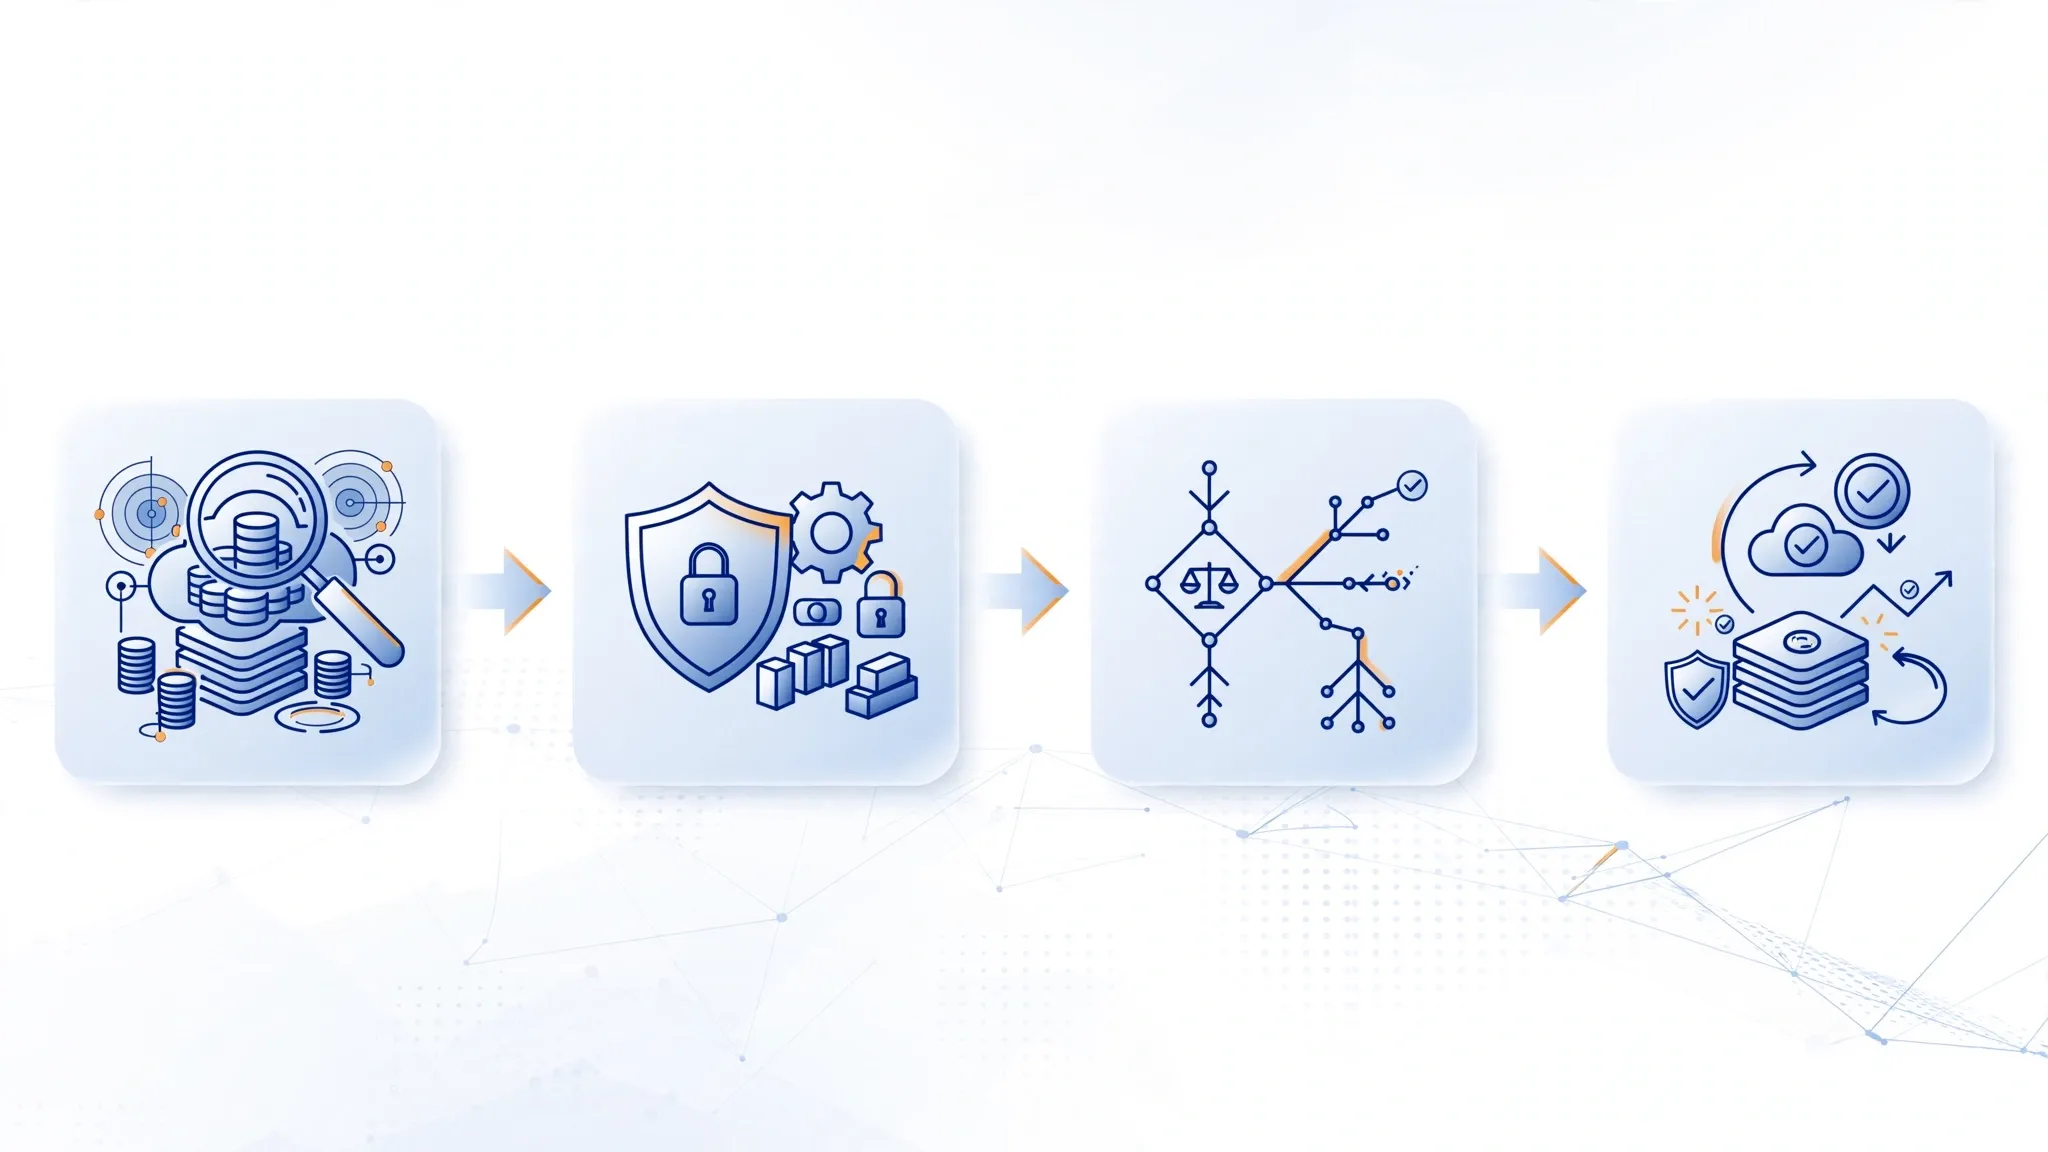
Short answer: A successful backup does not prove recoverability; test restores and validate RPO/RTO. Do not choose solely on hardware price or technology labels. Assess business criticality, outage risk, ownership and how outcomes will be verified. This guide provides a practical SME workflow with acceptance criteria.
BUSINESS CONTEXT
Why this matters to the business
Connect technical symptoms to operational impact
A small fault can spread across multiple services when asset inventories, dependency maps and change procedures are missing. Start with a register of assets, applications, owners, criticality, single points of failure, versions, suppliers and recovery options. Mark unknowns for validation rather than making assumptions.
IMPLEMENTATION
Assessment and implementation steps
Sequence the work with evidence and accountable owners
For every step, retain baseline evidence, identify an approver and set a review date. If internal expertise is limited, use an independent assessor while retaining business ownership of data, administrative accounts and risk-acceptance decisions.
PRACTICAL CHECKLIST
Actions to take
Apply these actions to critical workloads first.
Classify critical data and services
Assign an owner, capture evidence and define a pass/fail criterion.
Set business-driven RPO and RTO
Assign an owner, capture evidence and define a pass/fail criterion.
Use isolated or immutable copies where appropriate
Assign an owner, capture evidence and define a pass/fail criterion.
Review access to backup systems
Assign an owner, capture evidence and define a pass/fail criterion.
Test file, database and full application restores
Assign an owner, capture evidence and define a pass/fail criterion.
Measure actual recovery time
Assign an owner, capture evidence and define a pass/fail criterion.
Keep test evidence and update runbooks
Assign an owner, capture evidence and define a pass/fail criterion.
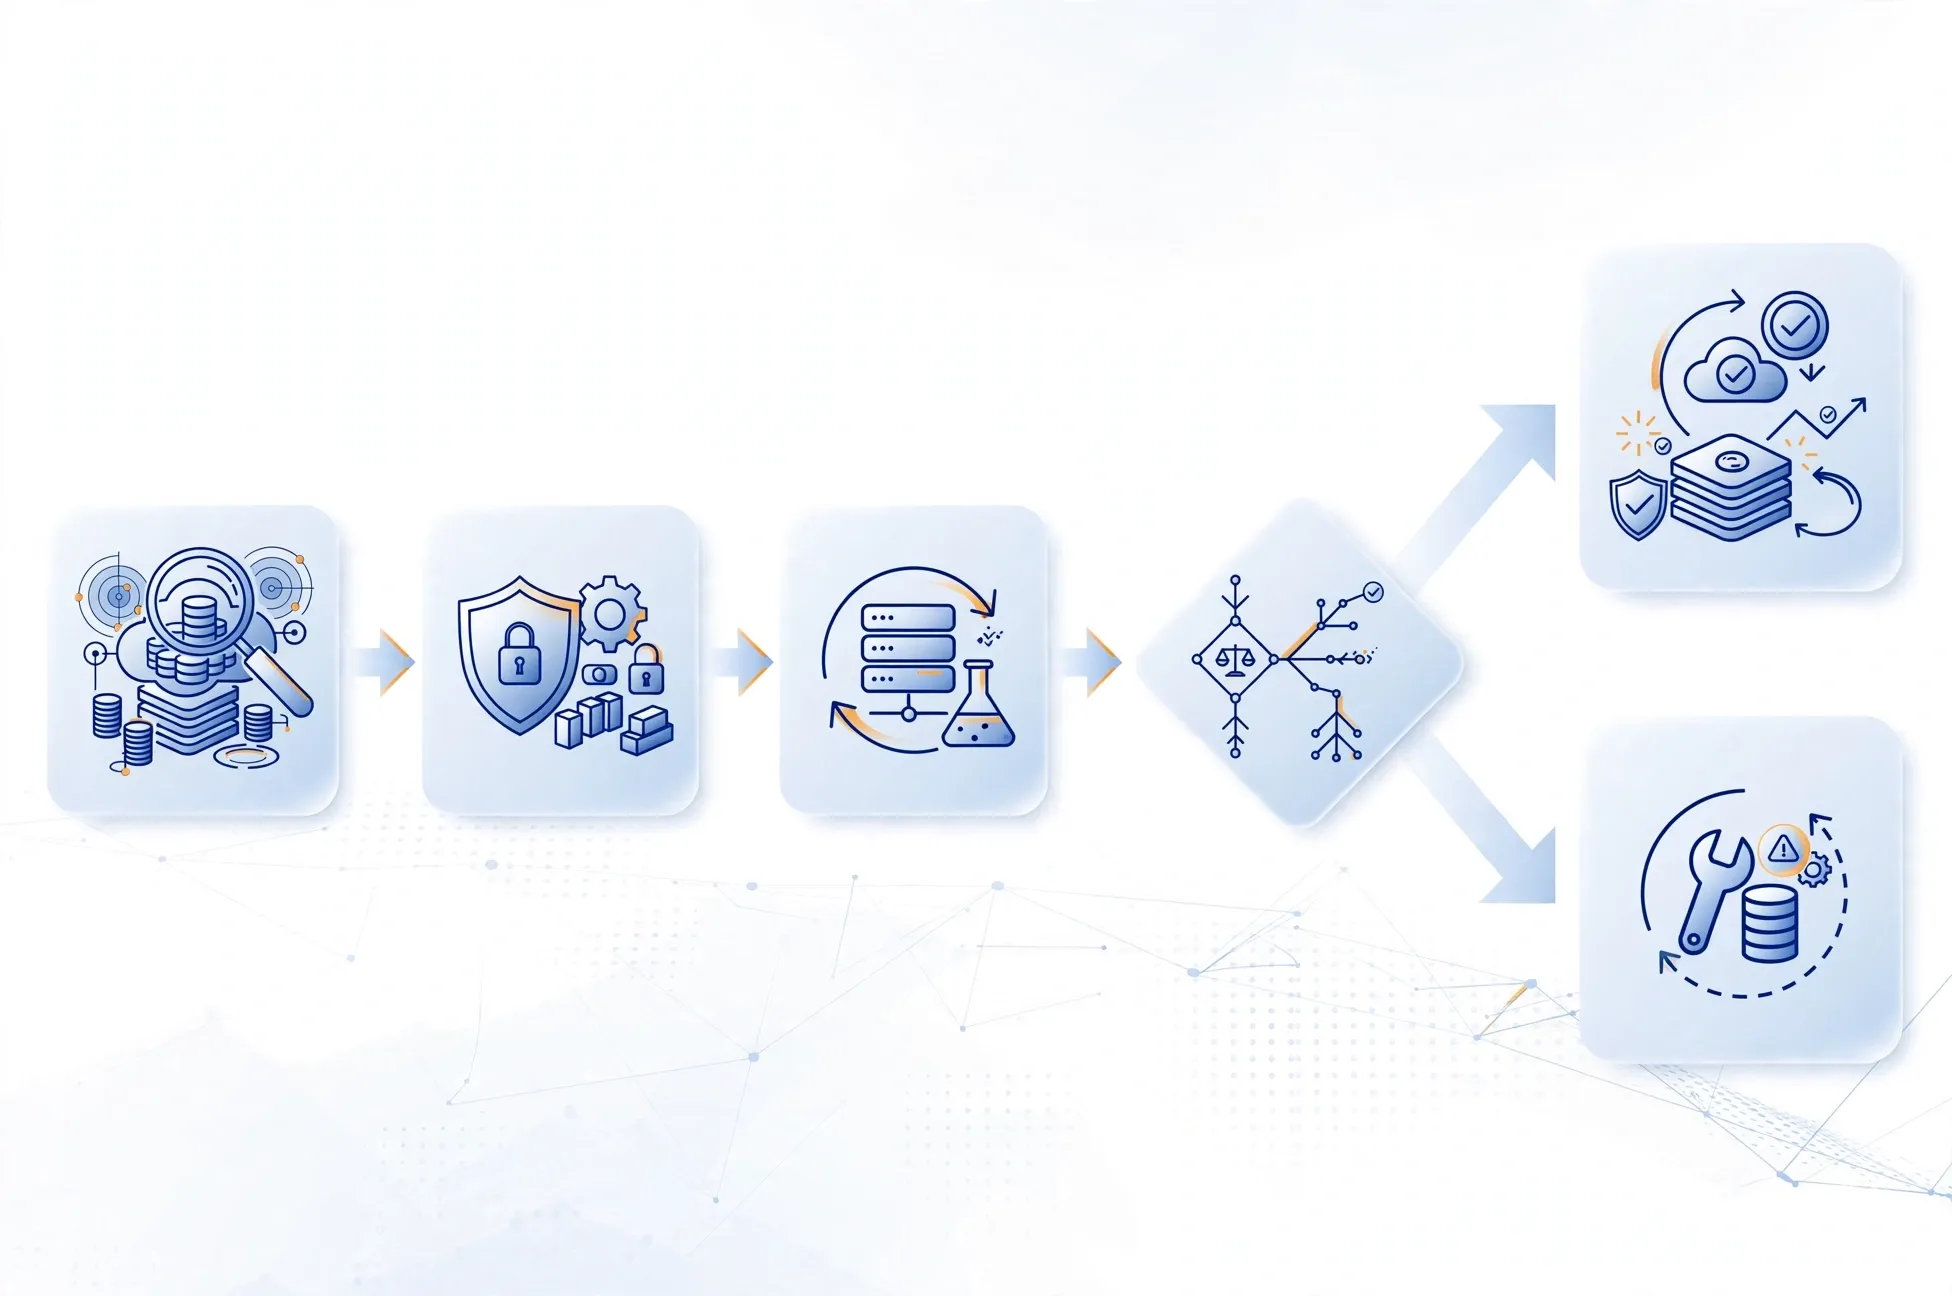
WORKFLOW
Decision and delivery flow
A visual reference for cross-team review
GOVERNANCE
Risk controls and acceptance
A change is not complete until recovery and handover are verified
Acceptance checklist: (1) A pre-change baseline exists; (2) functional, performance and security tests are documented; (3) suitable backup/rollback is available and tested; (4) least-privilege access is enforced; (5) monitoring and incident ownership work; (6) architecture, runbooks and handover records are delivered. Record justification and approval for any non-applicable control.
Operational measurements: track service availability against defined objectives, incident counts by severity, detection and recovery time, change success, restore-test results and actual spend versus budget. Tie metrics to business impact and specify measurement methods and reporting cadence; do not present a generic number as a universal SLA commitment.
Avoid these mistakes: buying tools before diagnosing the problem; losing account ownership; migrating everything at once; skipping rollback tests; generating alerts without an on-call owner; treating backups as a complete disaster recovery plan; and selecting vendors on price alone. Pilot first, verify outcomes and expand by risk.
FAQ
Frequently asked questions
Answers to common questions before committing
Does a small business need every control immediately?
No. Prioritize revenue-critical systems, sensitive data and operational continuity, then phase the work by risk.
Where should we start without current documentation?
Build an inventory and dependency map, interview operators and validate assumptions before making changes.
How do we evaluate return on investment?
Compare total cost, downtime, exposure and operational effort before and after using consistent measurement.
Can we outsource operations and retain control?
Yes. Define ownership of accounts, data, logs, approval rights and exit procedures in the agreement.
TALK TO FLOWNEXA
Start with an infrastructure assessment
FlowNexa can help clarify scope, risks and suitable implementation options. An initial discussion is not a purchase commitment.
Prepare
Critical systems, current issues and priorities
Next step
Agree on assessment scope and expected deliverables
